Kubernetes Security in the UAE: Securing Cloud-Native Environments with Dynatrace
Kubernetes solved a real problem for UAE businesses. Deploy faster. Scale on demand. Run containers instead of whole virtual machines. But it also created a new problem. Pods spin up and vanish in seconds. Namespaces multiply fast. A security team used to scanning fixed servers now faces a moving target.
IT Valley is a certified Dynatrace partner in the UAE. This post covers a side of the platform we don’t talk about as much as observability. Its security side, and how it applies to Kubernetes.
Why Kubernetes Breaks Old Security Tools
Most old security scanners were built for something that stays still. A server. A VM. A fixed IP address. Kubernetes doesn’t work that way. A pod might live two minutes. A namespace might spin up fifty containers, then shut them all down an hour later.
Scanning on a schedule misses all of this. By the time a nightly scan runs, half the containers are already gone. New ones have taken their place, and nobody’s checked them yet. UAE businesses running real workloads on Kubernetes need something that watches all the time. Not something that checks in once a day.
Runtime Security: Watching What’s Actually Happening
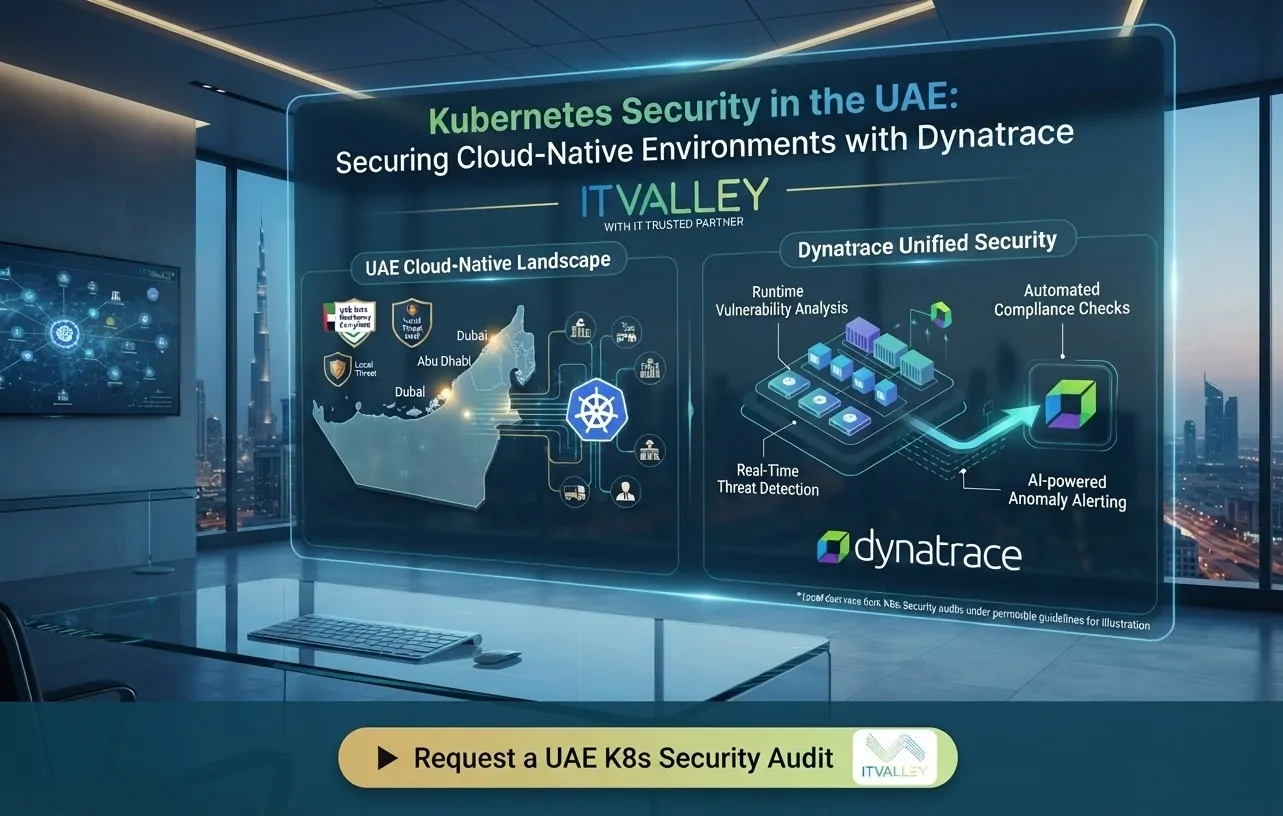
Dynatrace takes a different approach. Instead of scanning on a schedule, it watches your Kubernetes setup in real time. Every pod, every namespace, every service gets tracked live, not as a snapshot from last night.
That matters for one specific risk. A flaw that looks harmless in a static scan can turn dangerous once it’s actually reachable at runtime. Dynatrace flags real exposure. Not just a long list of theoretical issues sitting in a report nobody reads.
Davis AI: Cutting Through Alert Noise
Kubernetes setups throw off a lot of noise. Security tools stacked on top usually add even more. A UAE security team can end up drowning in alerts. Most turn out to be duplicates, or edge cases nobody needs to worry about.
Davis, Dynatrace’s AI engine, connects events instead of just listing them. It links a flaw to the services it actually touches, and to what happens if someone exploits it. Instead of a hundred scattered alerts, a team gets one clear picture. Here’s the real risk. Here’s what it touches. Here’s what to fix first.
Seeing the Full Attack Path
A flaw rarely stays inside one container. It moves. A weak point in a public-facing service can open a path into internal systems, databases, and other pods that were never meant to be exposed.
Dynatrace maps these attack paths on its own. It uses the same map data it already builds for observability. That’s a real edge. The security team isn’t working from a separate, disconnected chart. They’re looking at the same live picture the operations team already trusts.
Where This Fits for UAE Compliance
CBUAE and DIFC rules now expect more than a checkbox firewall. Regulators want proof an organization can spot and respond to threats. Not just a written policy sitting in a drawer.
Live runtime monitoring gives UAE businesses something real to show during an audit. Not a static document, but live proof of what’s actually being watched, and how fast issues get caught.
How IT Valley Deploys Dynatrace Security for Kubernetes
Environment mapping first. We map your Kubernetes clusters and namespaces before we set any security policy.
Live monitoring, not scheduled scans. Security visibility that updates as your setup changes, not once a night.
Davis AI tuned to your setup. Rules built for your real services, not left on generic defaults.
Ongoing support. Policy tuning, alert review, and reporting stay part of the relationship. Not a one-time job.
Frequently Asked Questions
Does Dynatrace replace our current vulnerability scanner? Not always. Dynatrace adds live context a static scanner just can’t give you. Many UAE clients run both. They use Dynatrace to rank what really matters among the flaws a scanner finds.
Can Dynatrace security work with our current observability setup? Yes. If you use Dynatrace for APM and monitoring already, security runs on the same data. No new platform to manage.
How fast can a Kubernetes security issue get flagged? Live monitoring means detection happens as the event occurs. Not on the next scheduled scan. Response time then depends on your team’s process, but detection itself never stops.
Talk to IT Valley About Kubernetes Security
Running real workloads on Kubernetes without live security checks is a real gap. Get in touch with IT Valley’s certified Dynatrace engineers for a straight read on what your UAE setup actually needs.